
Introduction
My employer Best Software Consultants B.V. organized a demonstration from LiquidWare about their product ProfileUnity. After that, I was enthusiastic about Profile Unity that I decided to give it more attention. So, I installed it on my lab environment and tested it thoroughly.
In this blog article, I will describe all the steps to install and configure ProfileUnity on a domain environment.
Technical background
About Profile Unity a copy-and-paste from the LiquidWare website: "ProfileUnity provides policy, profile and security management enabling portability across all Windows OS workspaces as well as physical, RDS, virtual and cloud." To deliver applications to the end-user, FlexApp is used. In short: during the logon process virtual disks with the application are mounted.
Preparation installation ProfileUnity
Profile Unity takes care of delivering the applications to the end-user. I installed Profile Unity on my SCCM server. And I used the ProfileUnity web interface to administer ProfileUnity from my domain controller. My domain controller is my management server...
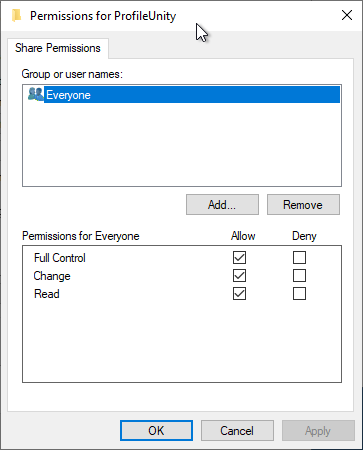
ProfileUnity stores all the files on a folder on the NETLOGON share. That is a good solution as it reduces network traffic. However, I decided to install all the files on a dedicated share, called ProfileUnity. The share- and NTFS-rights:
|
Share permissions |
NTFS permissions. I added Domain Computers so each computer can install the agent during the boot process. |

Installation Profile Unity
As mentioned earlier, these steps have been done on my SCCM server.
|
Start the installation via the executable ProfileUnity-Net_6.8.4_G4.exe.
Select the language you want to use during the installation phase. In this case English. Click [Ok]. |
|
Click [Next] |
|
Click [Next] to install the required applications. |
|
Click [Next] |
|
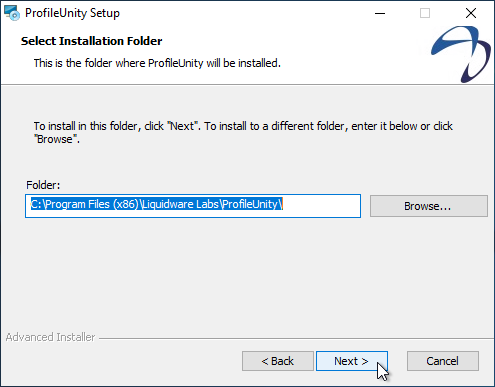
Accept the default path and click [Next]. |
|
Enter the details and click [Next]. |
|
I have selected 'Other' as I am using HyperV. And I will use the logoff script to make sure all the user settings are stored. |
|
Read the EULA carefully. Select 'I accept the terms in the License Agreement' and click [Next]. |
|
Click [Install] to start the actual installation. |
|
Click [Finish] after the installation. |




Configuration
During the configuration phase, the following is set:
- Default share for the files
- Setting up the default configuration
- Configuring settings via group policy objects
Configuration - default share
After a successful installation, you are prompted to fill in the following details:

The share \\demo-sccm\ProfileUnity has been created earlier.
Configuration - set up the default configuration
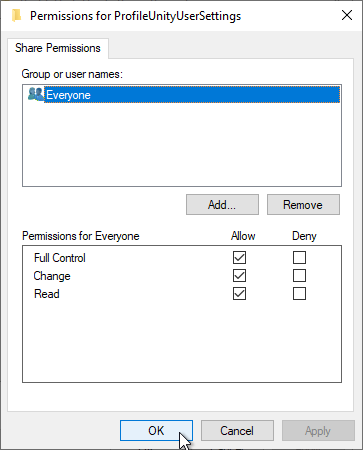
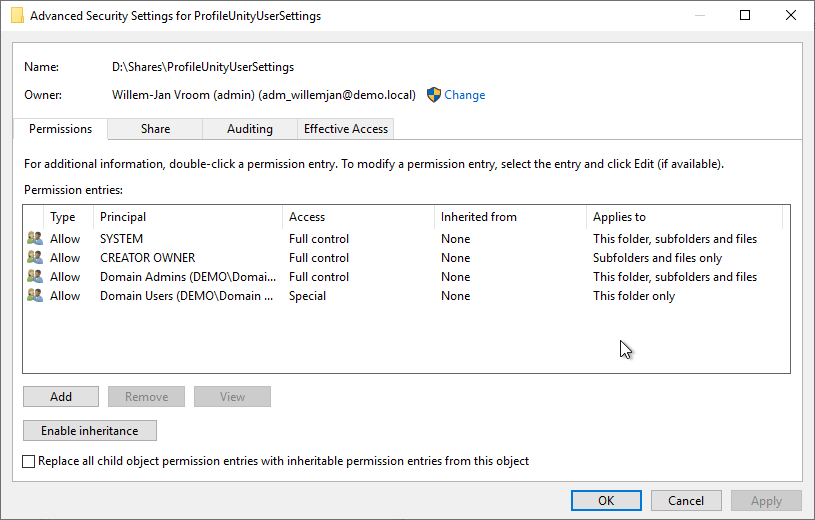
Now, configuring ProfileUnity. Before we start, we have to create the location where ProfileUnity stores the user settings. In this scenario I created the share ProfileUnityUserSettings:
|
Share permissions. |
NTFS Permissions |
|
Special NTFS permissions for Domain Users. |

|
Login to the web interface. Click left on [Configuration Management]. After that, click [Create] on the upper right corner. |
|
Click [Guided] |
|
I selected [Windows 7, 1, 2016 or 2019 as a Desktop and 2016 & 2019 RDS Full Desktop]. |
|
Click [Next] |
|
Specify where the user settings should be stored. The share ProfileUnityUserSettings has been created earlier. |
|
Skip the GPO Integration. It is done later manually. The advantage of doing it manually is that you are more in control. Thus click [Next] |
|
Click [Yes] to continue. |
|
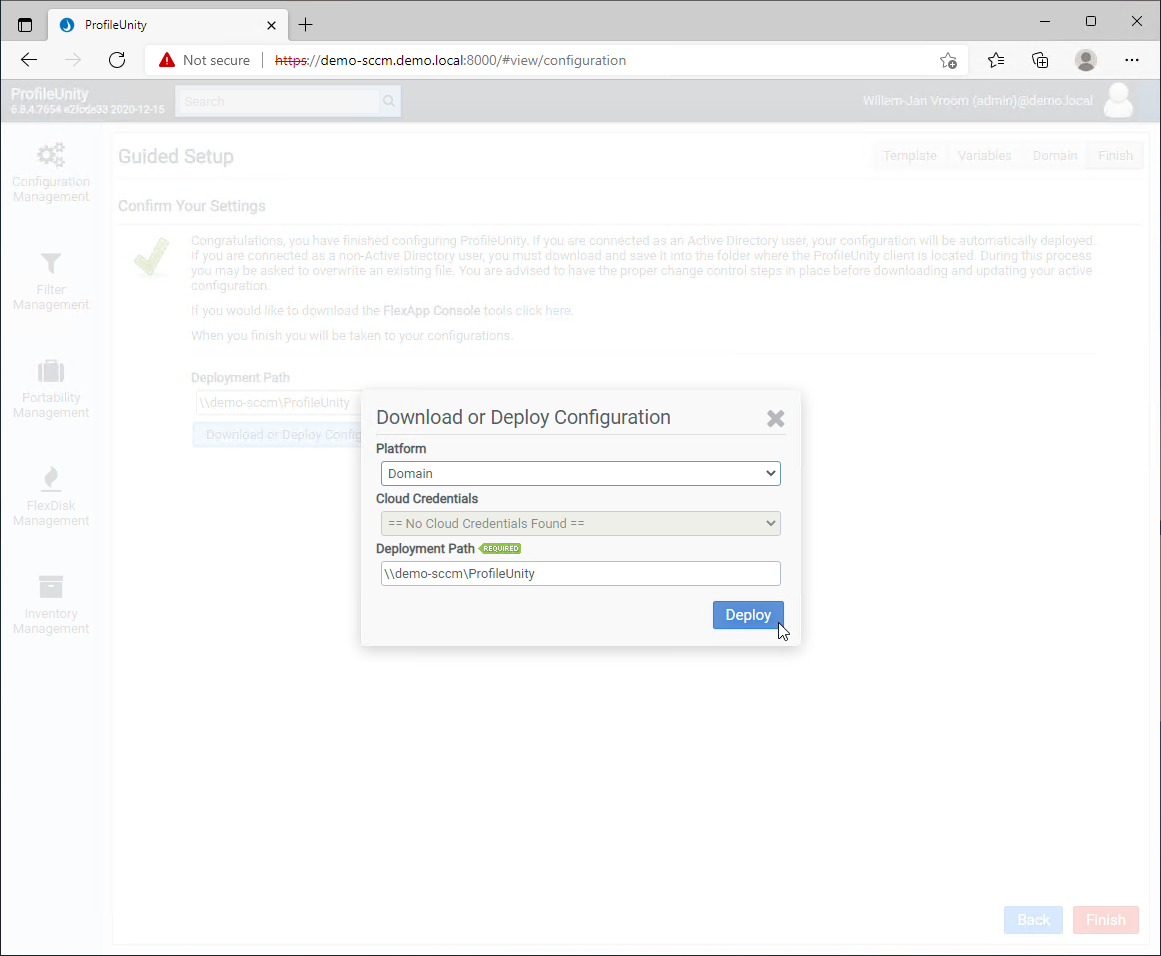
Click [Download or Deploy Configuration]. The ProfileUnity share is filled with all the needed files. |
|
Click [Deploy] |
|
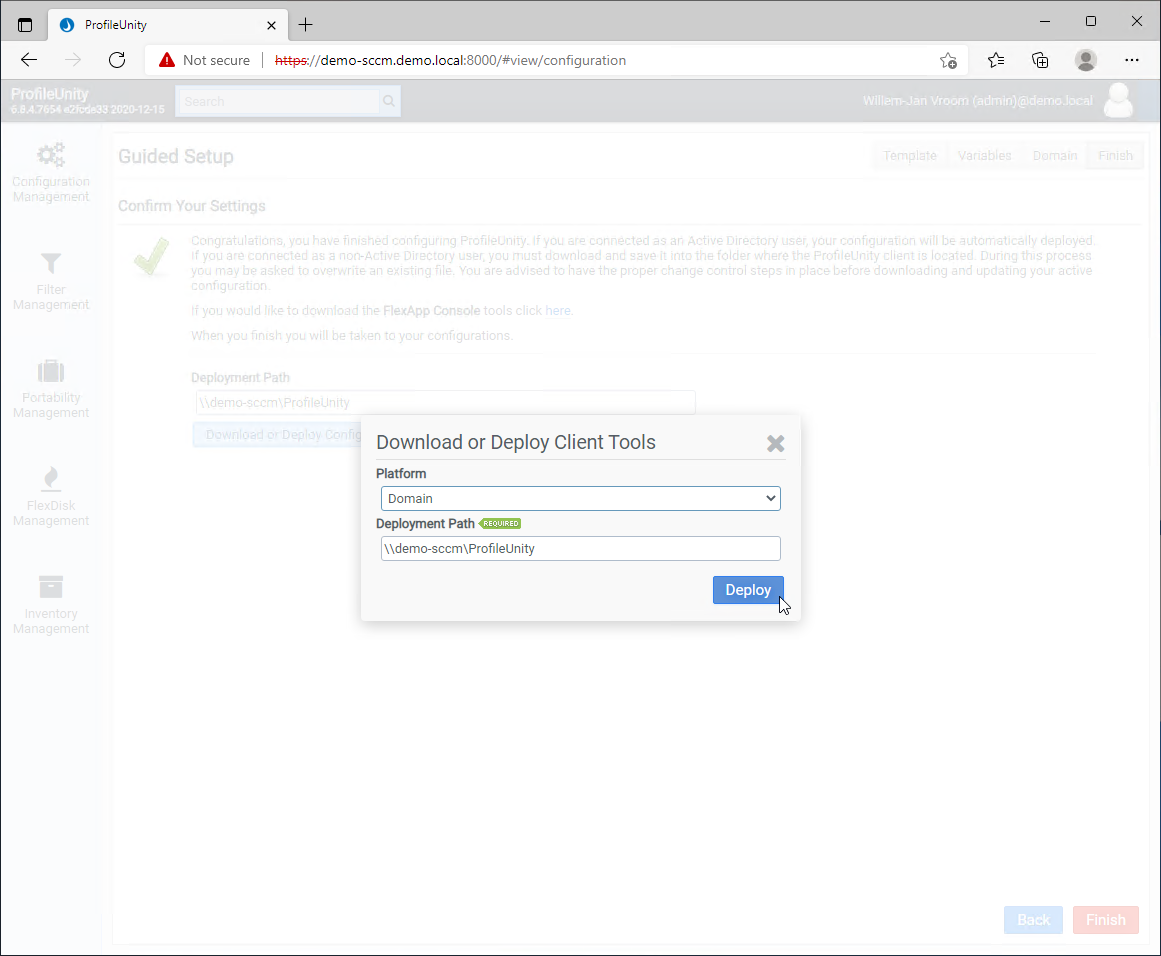
Click [Download or Deploy Client Tools] |
|
Click [Deploy]. |
|
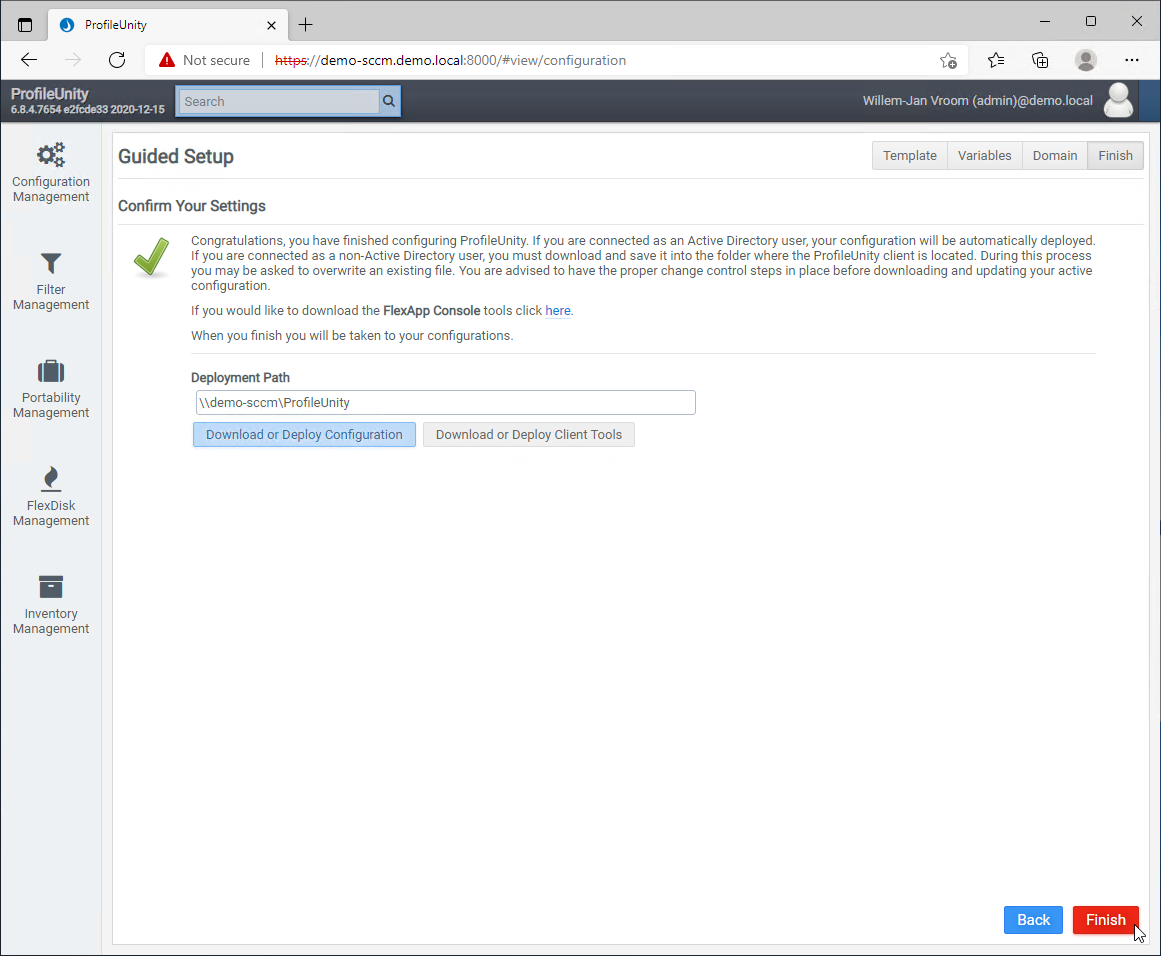
Click [Finish] |
|
The end result. Click on the line. |
|
And you see the default configuration. |





Configuration - group policy objects
Now, the final part. We want to configure the following for the domain-joined computers and domain-joined users:
- Domain joined computers:
- Script to install the client during the startup process
- Configure the paths to be used
- Domain joined users:
- Enable ProfileUnity
- Configure some paths to be used
- Silent or not?
Configuration - Domain joined computers
|
Start Group Policy Management Console and create the group policy object Computer - ProfileUnityStartupScript:
|
|
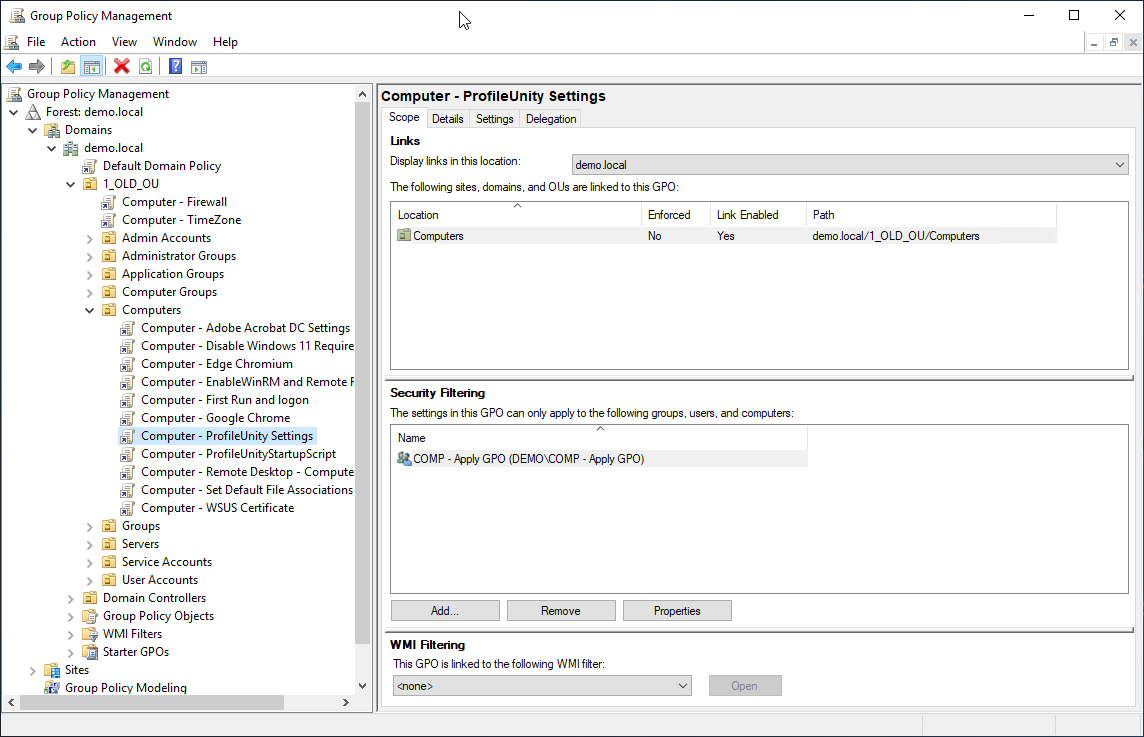
Create the group policy object Computer - ProfileUnity Settings:
|
|
Select the group policy object Computer - ProfileUnityStartupScript and set the name of the startup script. This script is run when the computer starts up. |
|
Select the group policy object Computer - ProfileUnity Settings. The following settings are set via an administrative template. Therefore, load the administrative template.
Click [Add] |
|
Select the .adm file from the ProfileUnity share and click [Open]. |
|
Click [Close] to add the template. |
|
These settings can be configured:
|
|
And a detailed overview of the settings. |



Configuration - Domain joined users
|
Start Group Policy Management Console and create the group policy object User - ProfileUnityLogoff Script:
|
|
Create the group policy object User - ProfileUnity Settings:
|
|
Select the group policy object User - ProfileUnityLogoff Script and set the name of the logoff script. This script is run when the user logs off. |
|
And the name of the logoff script. |
|
Select the group policy object User - ProfileUnity Settings and configure the above-mentioned settings accordingly. Add the .adm file if needed. |


Testing on a client
And now, testing on a client. We should see a Profile Unity progress bar when a user logs on:

And that is exactly what we need as we do not have any applications available now.
In the article ProfileUnity from Liquidware: deployment of a predefined application Firefox the steps to install a predefined application is mentioned.
Other articles in this series:
- [Article 1] - ProfileUnity from LiquidWare: installation and configuration
- [Article 2] - ProfileUnity from Liquidware: deployment predefined application Firefox
- [Article 3] - ProfileUnity from Liquidware: create a FlexApp Application
- [Article 4] - ProfileUnity from Liquidware: FlexApp Package Automation
- [Article 5] - ProfileUnity from Liquidware: create a FlexApp One Package
- [Article 6] - ProfileUnity from Liquidware: integration with Ivanti Workspace Control
- [Article 7] - ProfileUnity from Liquidware: Install Liquidware FlexApp ONE applications via Microsoft Endpoint Configuration Manager